Answer the board in euros, not in CVEs.
Under NIS2 your board approves the security measures and answers for them. Vardion gives it what it needs each quarter, from your own records.
For directors
What NIS2 asks of management
Approve the measures
Record who approved each policy and when, and have each director acknowledge the quarterly board pack from their own account.
Oversee them
Know where the programme stands and what is overdue.
Follow training
Track management training as a recurring duty, with the date of each round.
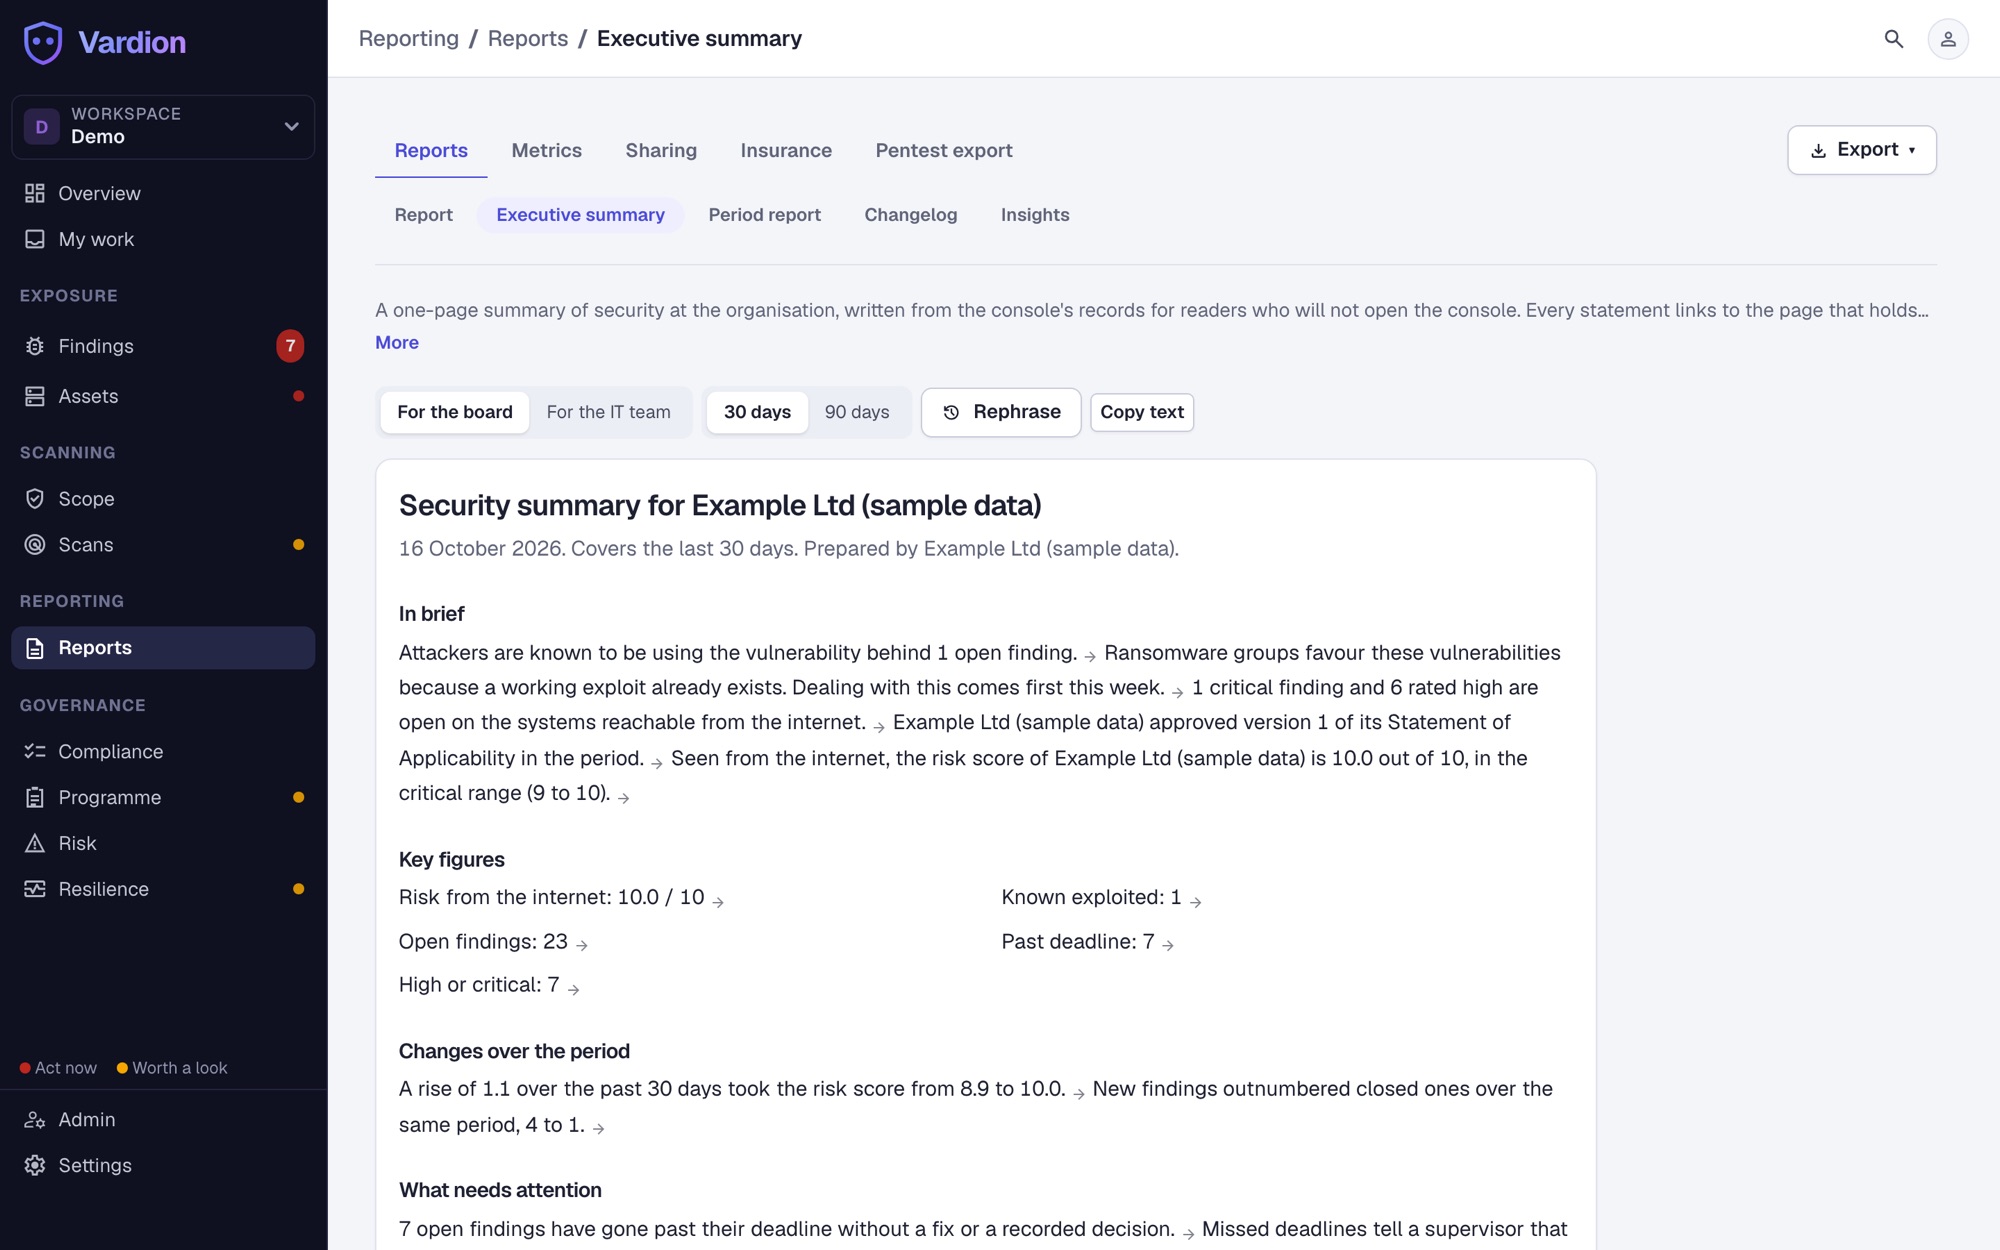
A summary your managing director will read
One page: the score, the main risks, what changed and what the board must decide.
- A version for the board and one for the IT team
- A full PDF report for anyone who will not open the console
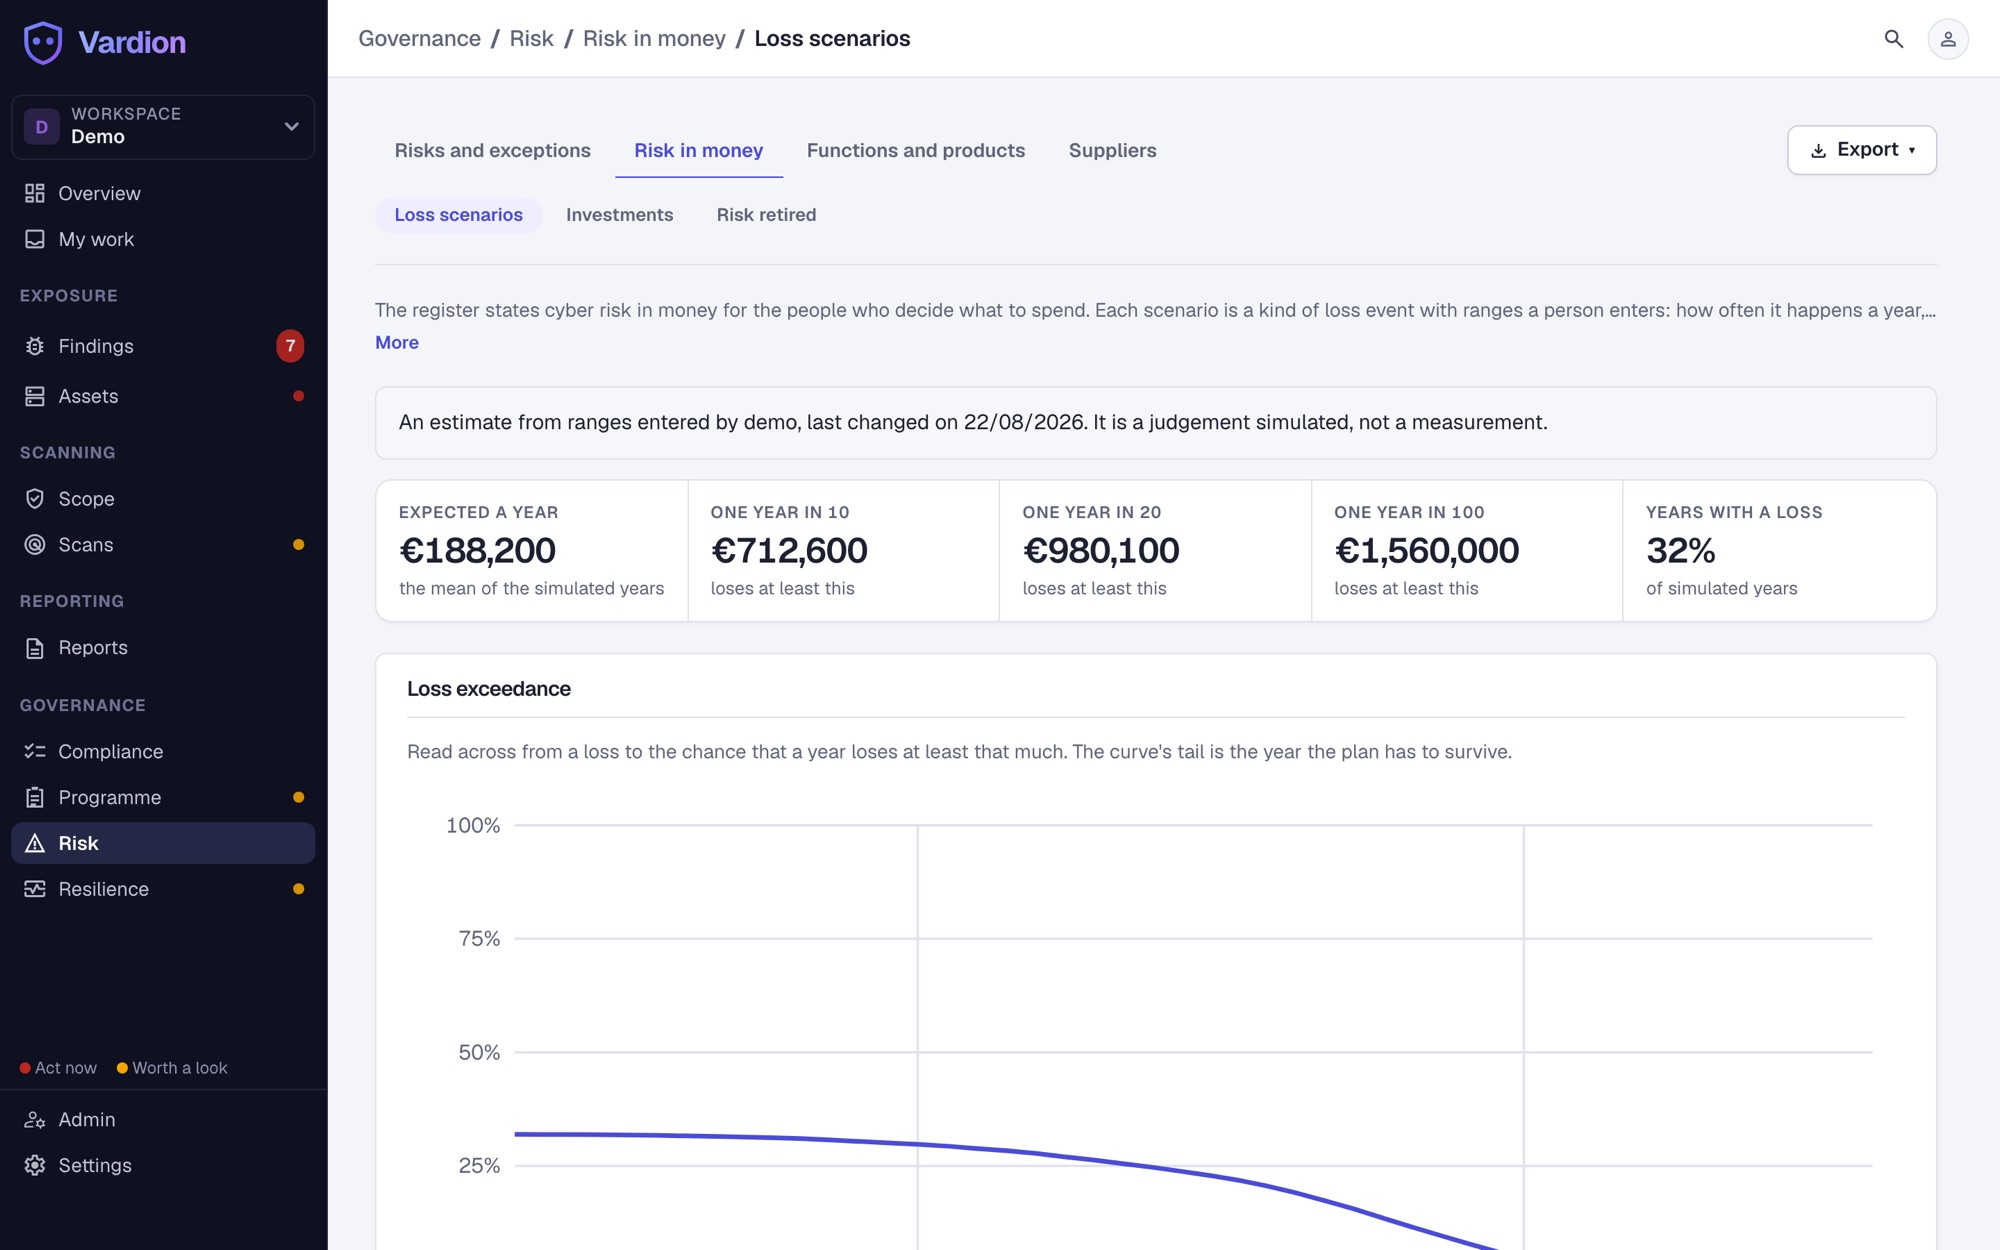
What a breach would cost
See the expected loss a year and the one-in-100-year loss.
- Built on FAIR, the method that measures risk in money
- See which control removes the most loss for each euro it costs
More answers, less writing
Ready before the board asks
Count the days at zero
Days in a row with no known exploited flaw open on the internet.
Spot where risk gathers
The address, owner or product where risk concentrates.
Show how fast you fix
Median time to fix and the share fixed on time.
A monthly summary by email
The score, what opened and closed and the coming deadlines.
FAQ
Reporting questions
Where do the euro figures come from?
From ranges your team enters for how often a loss happens and what it costs. The scans flag when a scenario's likelihood should rise.
Does it help with insurer and customer questionnaires?
Yes. It answers common security questions from insurers and customers from your scans, and shows what an insurer would see before your renewal.
What can attackers see on your domain today?
Find out in under a minute, then choose how to go further.
Partner programme
Run monitoring and compliance for your clients under your own brand.
See the partner programme