Get NIS2-ready without the spreadsheets.
Vardion turns NIS2, KYA 1689/2025, DORA and ISO 27001 into one plan your team works through, with the evidence collected as you go.
Does NIS2 apply to you?
Who NIS2 covers
High-criticality sectors (Annex I)
- Energy
- Transport: air, rail and water, plus road authorities and traffic systems
- Banking and financial market infrastructure
- Health
- Drinking water and waste water
- Digital infrastructure and managed ICT services
- Public administration and space
Other critical sectors (Annex II)
- Postal and courier services
- Waste management
- Chemicals
- Food production, processing and distribution
- Manufacturing: medical devices, electronics, electrical equipment, machinery and vehicles
- Online marketplaces, search engines and social networks
- Research
Size
- Medium or larger: 50 or more staff, or turnover and balance sheet both above €10m
- Usually essential if large and in Annex I: 250 or more staff, or turnover above €50m and balance sheet above €43m
- Usually important: any other medium or large organisation in an Annex I or II sector
- Any size: DNS service providers, top-level domain registries and trust service providers, among others
Not in scope? Customers who are will still ask you for evidence as their supplier (Article 21(2)(d)), and Vardion answers from your own records.
For suppliers
Answer your customer's questionnaire from your records
Start from a template
Supplier due diligence or a DORA third-party review, item by item.
Answer from your records
Asset register, architecture, certificate scope and policies, plus the risk, incident, exception and processing registers.
Send one pack
Every answer and record together, with a checksum for each file.
The authority's NIS2 tools, ready to run
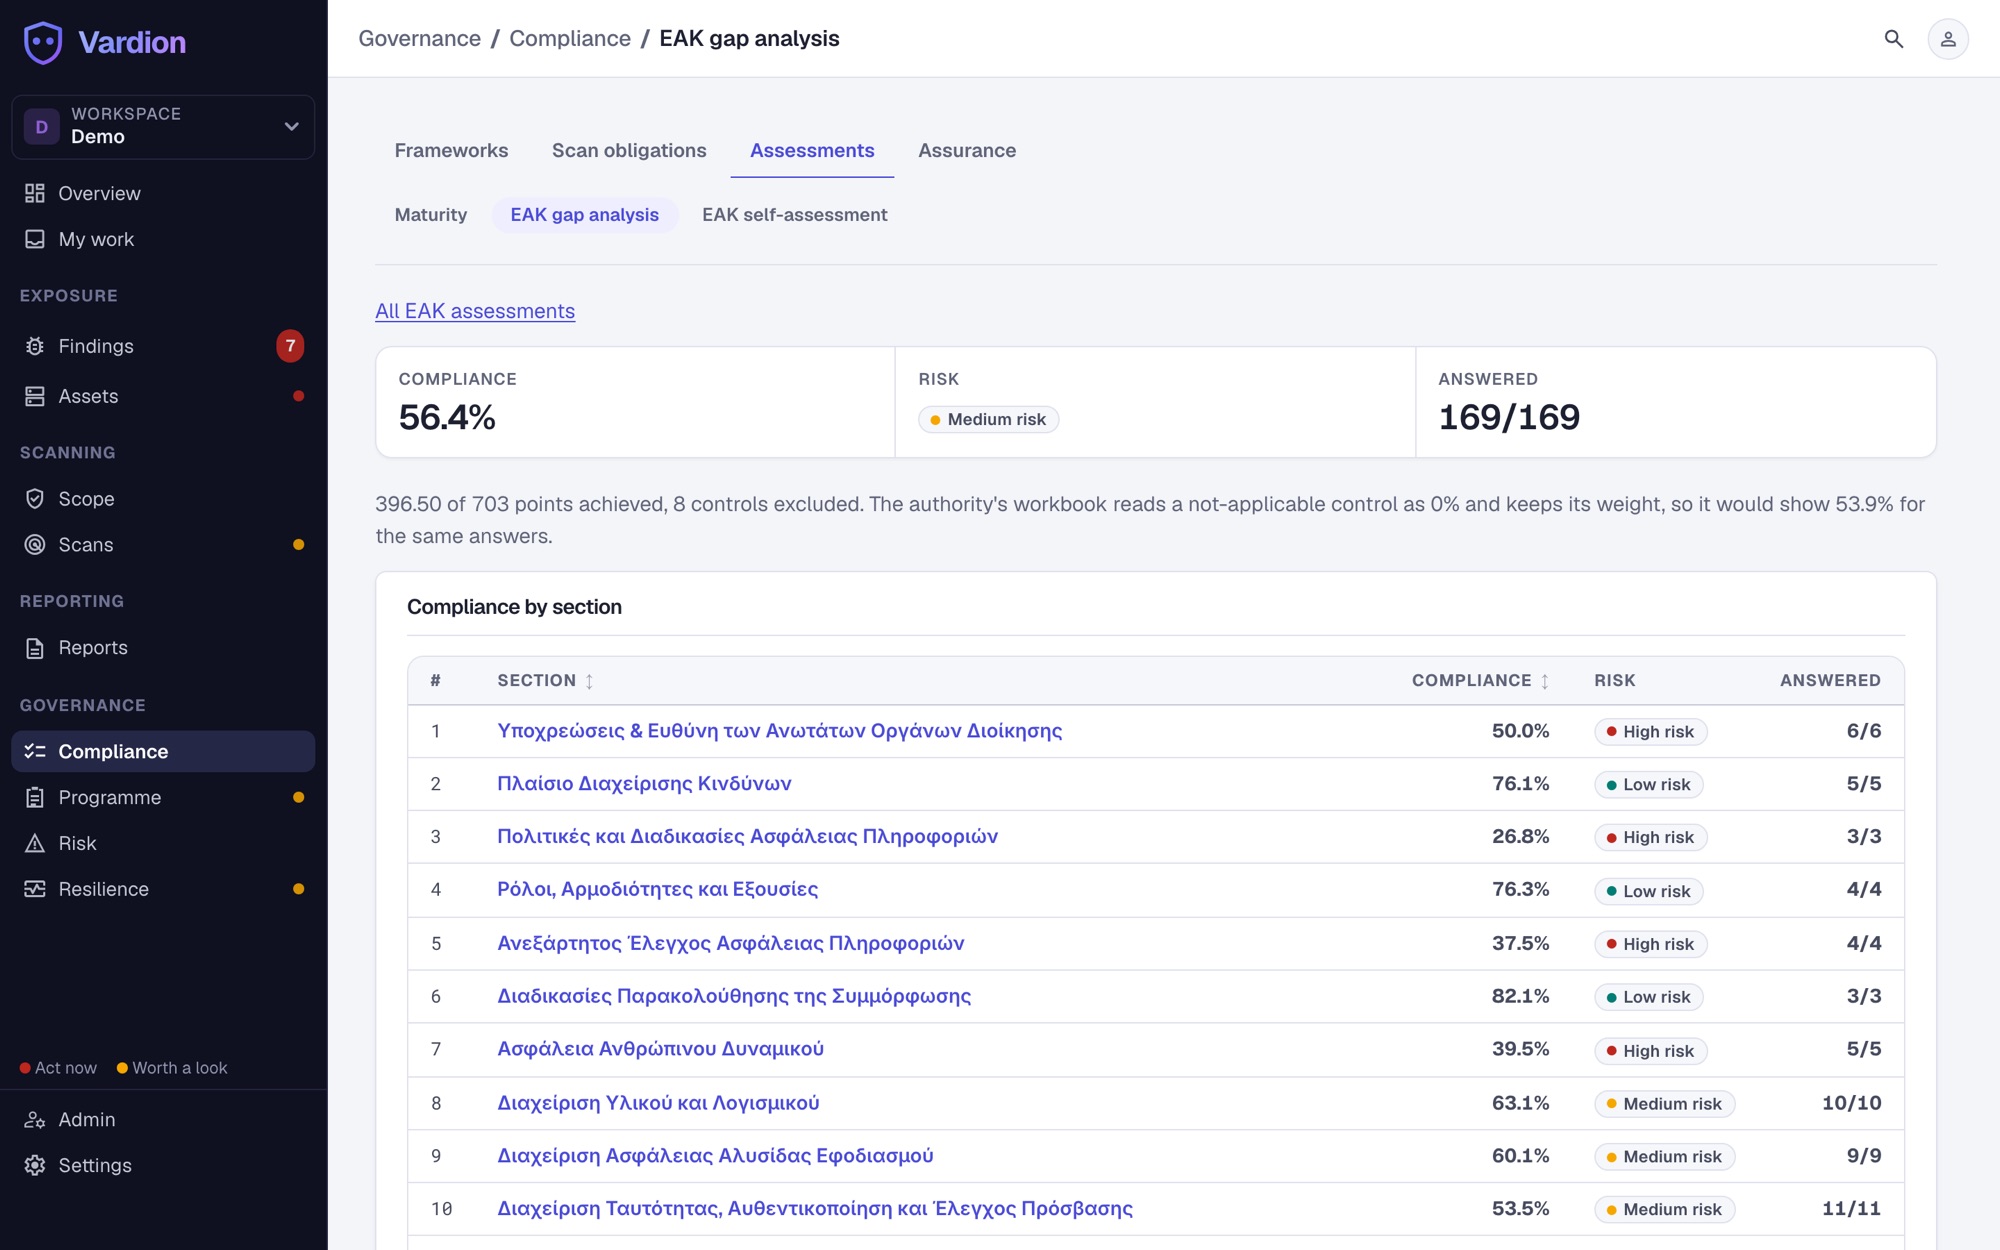
Work through the gap analysis and self-assessment of the National Cybersecurity Authority (ΕΑΚ) in its own Greek and watch your score rise as gaps close.
- Gap analysis: 169 controls in 24 sections, exported in the authority's own columns
- Self-assessment: 234 questions, scored as the authority's tool scores them, in the file that tool opens and saves
- Hand each section to the colleague who knows it
Beyond the assessment
Your whole programme in one place
Start from ready-made policies
16 policies and procedures, including the 12 that KYA 1689/2025 names, filled with your details, in Word.
Meet every reporting deadline
NIS2, GDPR and Cyber Resilience Act clocks, with notifications drafted from your facts.
Reuse your evidence
Link one document to every control it supports.
Keep risks under control
Risk and exception registers with owners and review dates.
Watch your suppliers
Weekly grades for key suppliers and questionnaires you send them.
Plan your recovery
Impact analysis, playbooks and 6 ready tabletop exercises.
Keep GDPR records
Processing records, impact assessments and data subject request deadlines.
Register your AI
Each AI system you use, checked against what the EU AI Act asks of you.
For financial entities
Bank, payment or investment firm? DORA comes first
File your register of information
Every missing mandatory field named by its code, and the EBA filing package ready to download.
Report ICT incidents on time
The 4-hour initial notification, the 72-hour intermediate report and the final report, each drafted from your facts.
Evidence your resilience testing
Your Article 24 testing programme, tracked against what was done.
Map your ICT providers
Each provider with its subcontractors, the functions it supports and how you would replace it.
Regulations and standards
One set of records for every rule you answer to
Also mapped to
The other frameworks your auditors use
FAQ
Compliance questions
How does Vardion help us comply with NIS2?
You complete the ΕΑΚ assessment, start from the policy drafts and log incidents with their deadlines, with each piece of evidence linked to its control.
Can our consultant work in the same console?
Yes. They run the assessment with you and review every answer before it counts.
Can we start on the hosted console?
Yes. Assessments, policies, registers and reports run there from day one, in Greek and English.
What can attackers see on your domain today?
Find out in under a minute, then choose how to go further.
Partner programme
Run monitoring and compliance for your clients under your own brand.
See the partner programme